Most developers who install an AI coding assistant assume it reads the files it needs. Few expect it to package the entire workspace and ship it somewhere else.
That’s what users say happened with ZCode, the AI coding assistant from Chinese AI company Z.ai, also known as Zhipu. After a week of public backlash, the company disabled the features involved, apologized, and brought in outside firms to confirm the data was gone, Reuters reported.
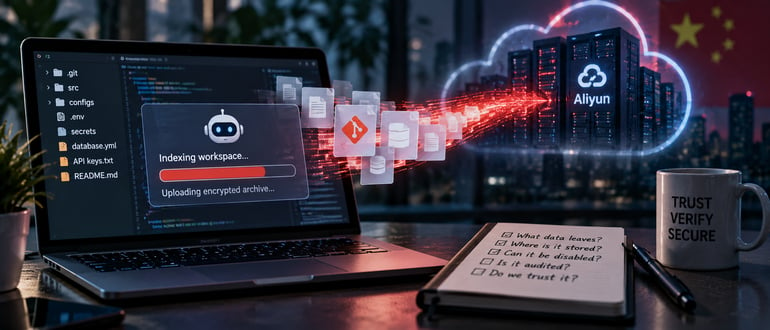
The trouble surfaced when an independent Chinese blogger who goes by Ferstar noticed abnormal disk usage and traced it to ZCode background processes. He found that whenever a user was logged in, ZCode packaged the entire workspace, including the full .git history, Git LFS cache, reflogs and global app configs. It then encrypted the bundle and uploaded it to Aliyun OSS, Alibaba Cloud’s object storage service.
The source was a Codebase Indexing feature that supported session checkpoints, version rollbacks, and wiki generation. It was on by default. According to Reuters, there was no toggle to turn it off, and the privacy policy didn’t disclose the behavior. The archives were compressed and encrypted with keys held only on Z.ai’s servers, so users couldn’t see what had left their machines.
One company, Chengming Technology, said six coding workspaces had been uploaded, including source code, database passwords and employee personal information. It later retracted the complaint, citing “wrong evidence,” without further explanation.
Z.ai apologized on Friday and said it had deleted the data. Many users weren’t satisfied. Because the archives were encrypted with the company’s own key, nobody outside Z.ai could verify that claim.
On Monday, the company went further. It disabled the upload mechanism in ZCode version 3.14.0, deleted the related cloud storage, open-sourced the assistant built on its GLM-5.3 model, and added zero-data-retention options. It also commissioned security assessments from the China Academy of Information and Communications Technology, a think tank affiliated with China’s industry ministry, and cybersecurity firm NSFOCUS. Z.ai said NSFOCUS confirmed that the stored data and the storage bucket itself had been deleted. Z.ai said the data “has never been used for model training” and pledged to “establish an ongoing product security vulnerability reporting and response process.”
It’s tempting to file this under “Chinese AI risk” and move on. That would miss the point.
This isn’t an AI model problem. It’s an old security architecture problem. Take away the AI, and you have a desktop app with broad file-system access, a background process that phones home, a default-on setting, and a privacy policy that didn’t match what the software did. What’s different now is access. AI coding assistants need deep context to be useful. So they sit inside the repository, next to .env files, credentials, commit history, and the customer data someone committed by mistake three years ago. And developers are adding these tools fast, often before security has signed off.
That’s what made this incident hard to spot. Mitch Ashley, vice president and practice lead for CIO & technology buyers and software lifecycle engineering at The Futurum Group, points to the timing. “The workspace uploads came to light because an independent blogger traced abnormal disk usage to a background process, well after developers had installed the tool,” he said.
The lessons here apply to every AI coding tool, no matter where the vendor is based.
First, treat coding assistants as privileged software. They deserve the same review as any agent with access to source code and secrets. Ask vendors exactly what leaves the machine, when, where it’s stored, and for how long. Second, check the defaults. Indexing, cloud sync, and “memory” features are often on out of the box because they make the product work better. Teams need to know which ones are active and whether they can be turned off centrally.
Third, watch the network. Egress monitoring on developer workstations should flag large compressed archives heading to an outside storage bucket. Fourth, keep secrets out of repos. Database passwords sitting in a workspace are a problem whether an AI tool uploads them or not. Secret scanning and vault-based credential management limit the damage when something like this happens.
Finally, favor tools you can verify. Z.ai’s decision to open-source ZCode came late, but it’s the right direction. Open code, documented data flows and independent audits give security teams something to check instead of something to trust.
For many companies, source code is their most valuable intellectual property. Having it land in a third party’s cloud without anyone deciding to send it is a business risk, not just a technical one. And deleting the data doesn’t settle every question. Ashley raises the one that remains open. “But has anyone answered the question of where those codebases went while in the cloud and how they were used?”
That risk will grow as coding assistants turn into agents that run commands, open pull requests, and act on their own. The more a tool can do, the more it can do by accident.
Z.ai’s eventual response covered the right steps: disable, delete, verify, open up. But the trust damage happened in the gap between what the product did and what users were told. DevOps teams can’t close that gap for vendors. They can make sure they ask the right questions before installing the next assistant.
from DevOps.com https://ift.tt/e0P3HR1
Comments
Post a Comment